> ## Documentation Index
> Fetch the complete documentation index at: https://cortex-foundation-add13747-droid-1a2462c9-cor-444-sanitize.mintlify.site/llms.txt
> Use this file to discover all available pages before exploring further.
# Cortex Security
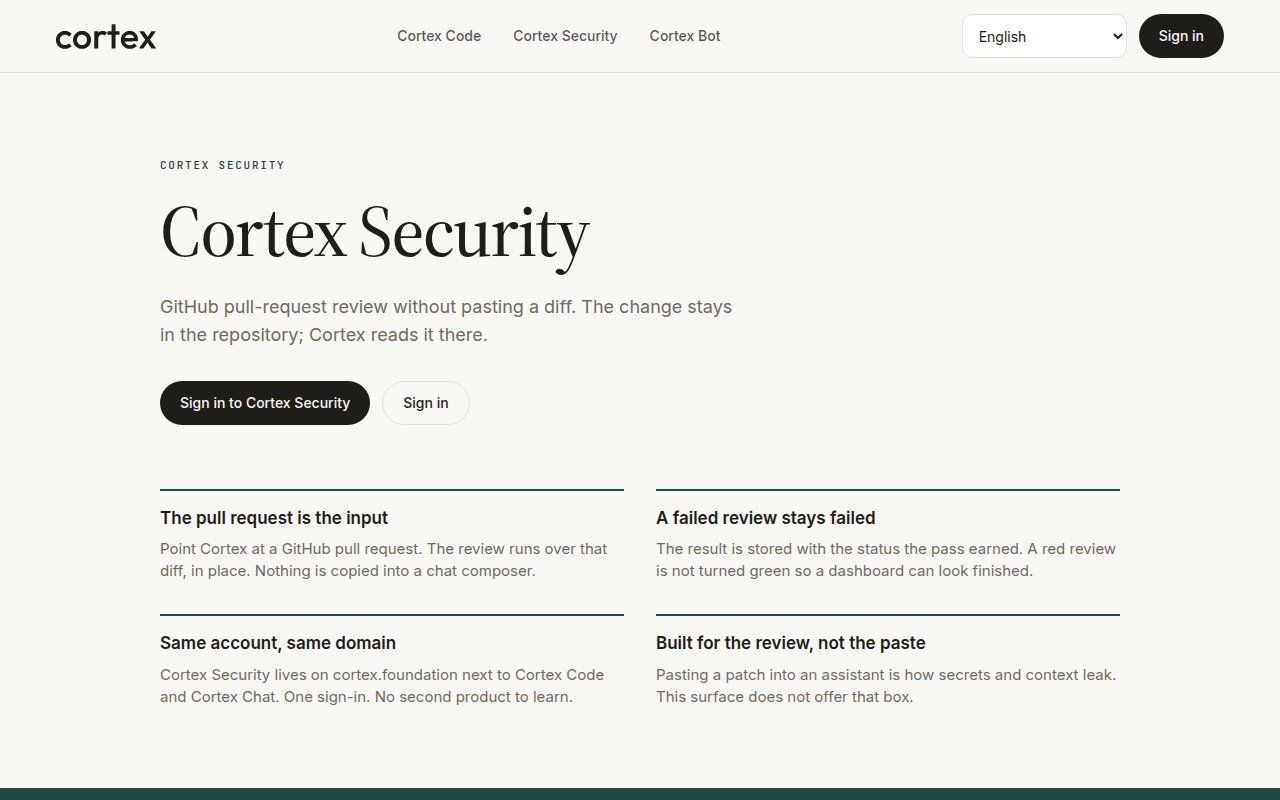
> GitHub pull-request review without pasting a diff. The change stays in the repository; Cortex reads it there and posts a check run that stays failed when it fails.
Cortex Security reviews GitHub pull requests in place. Install its GitHub App from the product, and each pull request gets one review pass posted as a check run named **Cortex Security**. A review that could not run is stored as failed — never rewritten as an approval so a dashboard can look green.
 ## Two routes, two things
| Route | What it is |
| ------------------------------------------------------- | -------------------------------------------------- |
| `cortex.foundation/security` | The public **product page** for Cortex Security |
| `/code/security` in the app | The signed-in **review inbox** |
| [Security and privacy](/security/overview) on this site | How Cortex handles your data — a different subject |
## Install and review
Choose **Code** in the product switcher, then **Security**.
From the inbox, install the app on the repositories you want reviewed. This is a separate install from [Connect GitHub](/code/github), which is for Code sessions.
Cortex reads the diff in place and posts a check run named **Cortex Security** with its findings.
Every review lands in `/code/security` with the status the pass earned.
 ## How a review behaves
| Behaviour | Why |
| --------------------------------------- | ---------------------------------------------------------------------------------------------------------- |
| One pass over the diff | A review is a pass, not a conversation |
| Failed stays failed | A review that could not run is stored as failed, never as approved |
| Nothing is pasted | Pasting a patch into an assistant is how secrets and context leak. This surface has no such box. |
| Policy is fixed by the repository owner | Policy lives at `/code/security/policy` in the app. A pull request cannot reduce the scrutiny it receives. |
## Cortex Security and the CLI
The CLI can run a review in CI from the working tree — `cortex exec --auto read-only --git-diff "review this diff"` — and `cortex github install` scaffolds the workflow. That is a headless Code run, not the Cortex Security GitHub App; use whichever fits your pipeline, or both. See [Headless runs](/cli/headless).
## Related
* [Connect GitHub](/code/github) — the other GitHub install.
* [Security and privacy](/security/overview) — data handling and sandboxes.
* [Troubleshooting](/code/troubleshooting) — what a failed check run means.